

Scaling Real-Time Features: WebSockets, Connections, and Infrastructure
Websocket connections, long-polling, and real-time features have become common expectations in modern web applications — live notifications, collaborative editing, chat, live dashboards. But real-time infrastructure introduces its own distinct set of scaling and reliability challenges beyond typical request-response web traffic. Here's what to actually plan for.
Why Real-Time Infrastructure Is Different
Traditional HTTP request-response traffic is inherently stateless and short-lived — a request comes in, gets processed, a response goes out, and the connection typically closes shortly after. WebSocket connections, by contrast, are long-lived and stateful — a single connection can remain open for the entire duration of a user's session, fundamentally changing how you need to think about server capacity, load balancing, and failure handling.
Connection Count Becomes a Primary Capacity Constraint
With traditional HTTP, server capacity is often primarily about processing throughput — how many requests per second can be handled. With persistent WebSocket connections, the number of simultaneous open connections a single server can maintain becomes a meaningful constraint in its own right, independent of actual message throughput, since each open connection consumes some baseline memory and file descriptor resources regardless of how much data is actually being actively transmitted through it at any given moment.
Load Balancing Requires Different Consideration
Standard round-robin load balancing, distributing each new request to a different server, works fine for stateless HTTP requests. For WebSocket connections, once a client establishes a connection to a specific server, that connection generally needs to persist with that same server for its full duration — meaning load balancing decisions matter primarily at initial connection time, and you need infrastructure that can route subsequent messages correctly to whichever specific server is holding each specific client's actual persistent connection.
Handling Server Restarts and Deployments Gracefully
A standard HTTP deployment can simply stop accepting new requests on an old server version and let existing short-lived requests complete naturally before shutting down. WebSocket connections, being long-lived, require more deliberate handling — either gracefully migrating active connections to new server instances, or having client-side reconnection logic robust enough to handle a server-initiated disconnection and cleanly re-establish a new connection without significant user-visible disruption to their experience.
Implement Robust Reconnection Logic
Network conditions are inherently unreliable — mobile connections drop, Wi-Fi hands off between access points, servers occasionally restart for maintenance or deployment. Client-side code needs to handle disconnection gracefully, implementing reconnection logic (typically with exponential backoff to avoid overwhelming your server with simultaneous reconnection attempts from many clients after a broader outage) so that temporary network hiccups don't require a full page reload or otherwise significantly disrupt the user's actual experience.
Consider Message Delivery Guarantees Carefully
Unlike a standard HTTP request, where the response either arrives or the request visibly fails, real-time messages can be lost during a brief disconnection window without either party immediately, explicitly realizing it happened. Depending on your specific use case's requirements, you may need to implement acknowledgment mechanisms, message queuing during disconnection, or reconciliation logic that syncs state once a connection is successfully re-established, rather than simply assuming messages sent during any connection gap are inherently, automatically synchronized once connectivity resumes.
Use a Dedicated Pub/Sub Layer for Multi-Server Setups
Once you're running multiple servers handling real-time connections, you need a mechanism for a message originating from one server (perhaps triggered by an action from a user connected to server A) to actually reach a different user who happens to be connected to server B. A shared pub/sub layer (Redis pub/sub, or a dedicated message broker) handles this cross-server message distribution, which becomes necessary infrastructure once you scale beyond a single server handling all real-time connections in isolation.
Monitor Real-Time-Specific Metrics
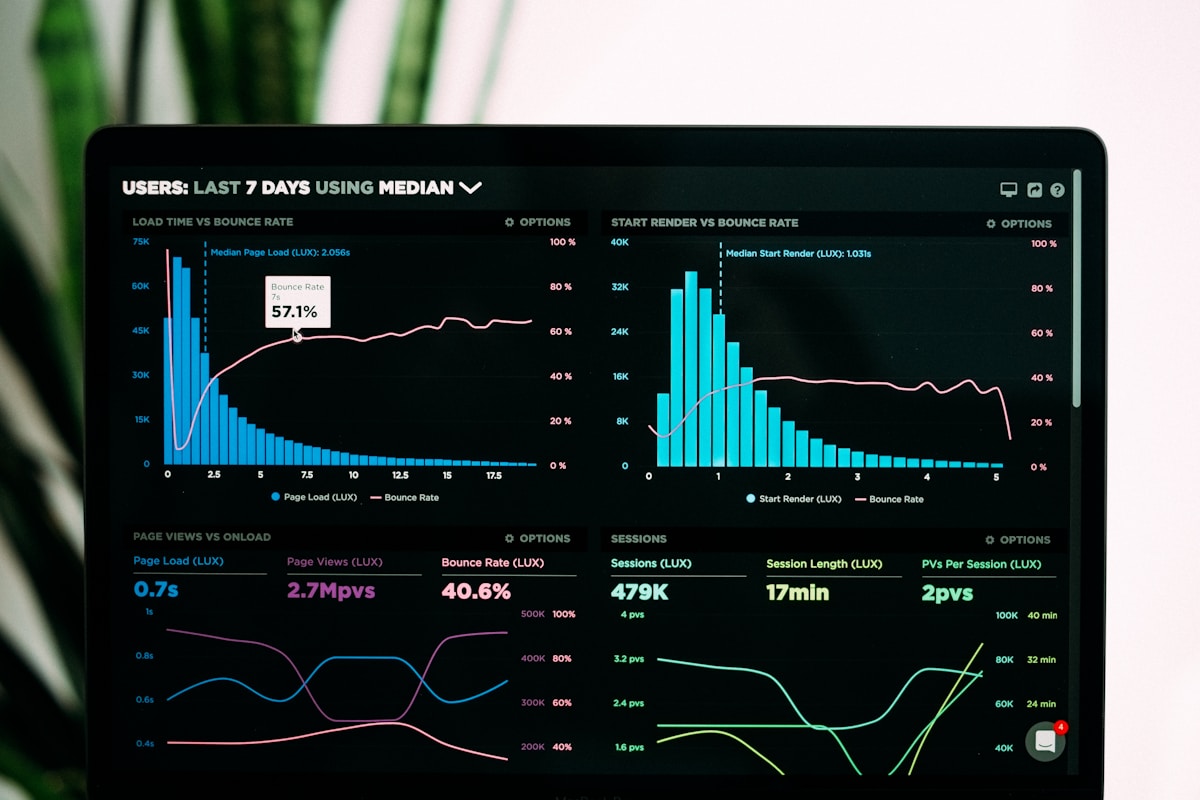
Beyond standard server metrics, real-time infrastructure benefits from specifically tracking active connection counts, message throughput, and reconnection rates. A sudden spike in reconnection attempts, for instance, might indicate an underlying instability issue affecting many users simultaneously that wouldn't necessarily be obviously visible through standard HTTP-oriented monitoring metrics alone.
Plan for Graceful Degradation
For genuinely critical functionality, consider what happens if real-time connectivity fails entirely for a given user — does your application degrade gracefully to periodic polling as a fallback, or does core functionality become completely unavailable? Building in at least a basic fallback path for real-time features, where practically feasible, provides meaningfully better resilience than a design that assumes WebSocket connectivity will always, reliably succeed without any planned alternative path.
The Bottom Line
Real-time features introduce genuinely different infrastructure considerations compared to traditional stateless HTTP applications — connection-oriented capacity planning, cross-server message distribution, and more deliberate reconnection and deployment handling all require specific, deliberate attention beyond what a typical request-response web application architecture would otherwise need to plan for.